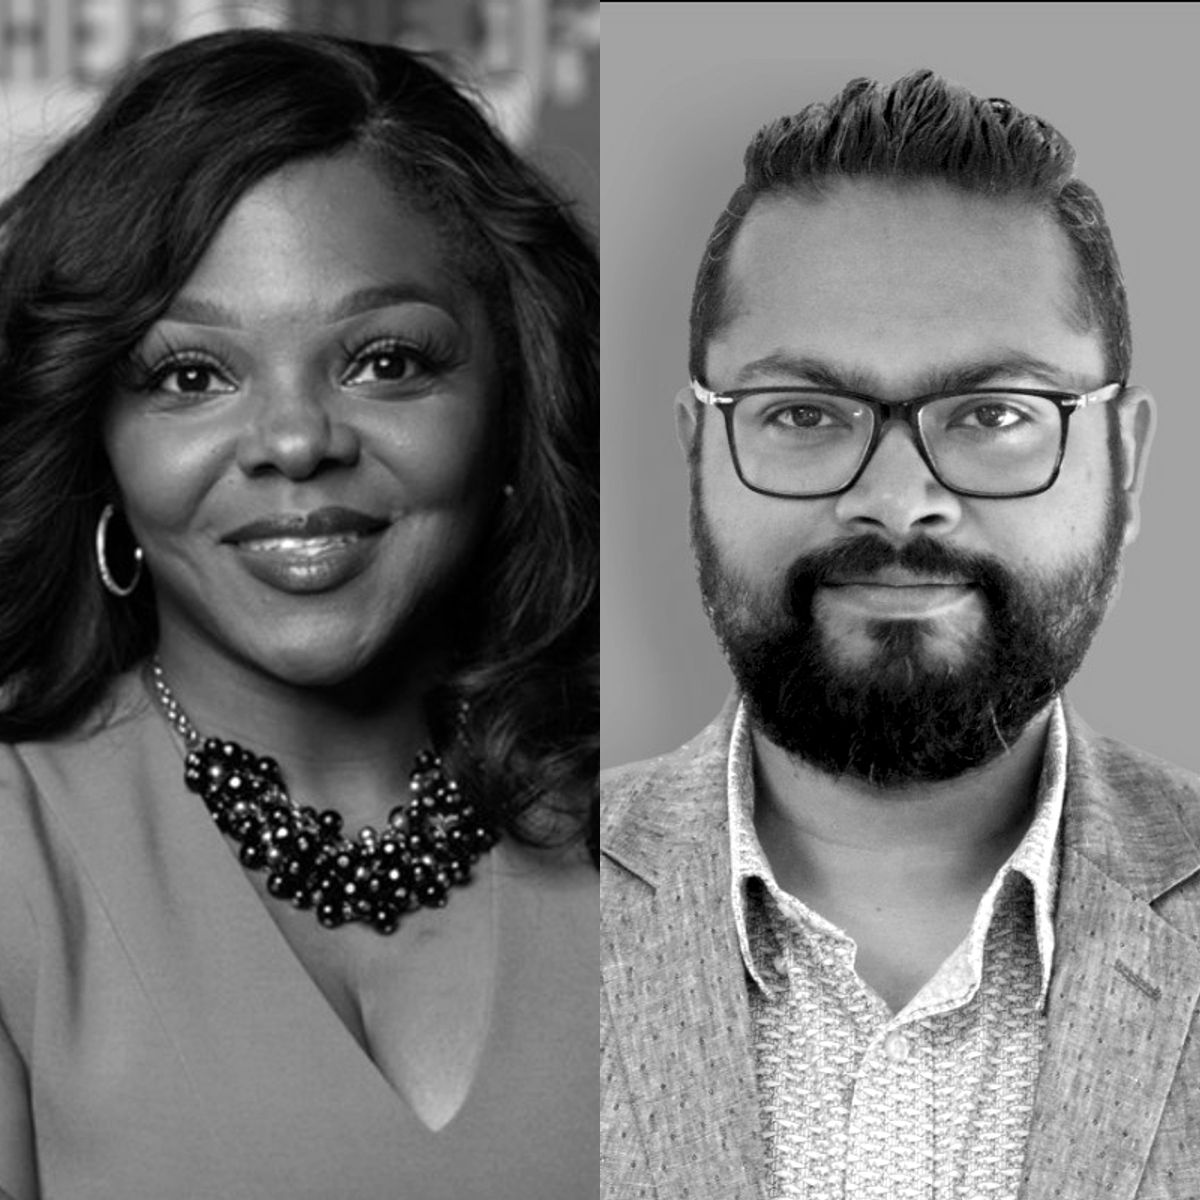
Agents Are Like Teenagers: Governing at Machine Speed with Mastercard's Dr. Jay & Arjun Ramakrishnan
Alissa Abdullah, PhD and Arjun Ramakrishnan · Deputy Chief Security Officer at Mastercard and Senior Principal Cybersecurity Architect at Mastercard
Alissa Abdullah, PhD ("Dr. Jay"), Deputy Chief Security Officer at Mastercard, and Arjun Ramakrishnan, Senior Principal Cybersecurity Architect at Mastercard, join us live from Black Hat to explain why access models built for humans start to break when agents act on their behalf.
You can't provision access for an agent the same way you provision it for an employee, and just-in-time authorization takes on a new meaning when the consumer operates at machine speed. Dr. Jay and Arjun explain why every tool call and action needs to be authorized, why that's difficult to enforce, and what security teams need when an agent goes rogue, including the ability to revoke access instantly through a button or API call.
We also get into Mastercard's three-layer framing of security for AI, from AI, and with AI, and why agent governance needs to move from periodic review to real-time enforcement.
Listen on
Transcript
DownloadRead the full transcript
Allie Howe Welcome to today's episode of the Insecure Agents podcast. I'm your host, Allie Howe, and today I'm super excited to be coming to you live from Black Hat. Today I have some very special guests with me. I have Arjun Ramakrishnan from Mastercard. He's a senior principal cybersecurity architect there. And I also have Dr. J. This is Alissa Abdullah commonly known as Dr. J. She is Mastercard's deputy, deputy chief security officer there, and she also holds a Ph- a PhD in information technology management, also has a master's degree as well in computer networks and a bachelor's in mathematics. I'm super excited to have them both with us today to tell us more about what they're seeing in AI security, how that's evolving in a place like Mastercard, and what their take is on Black Hat.
So without further ado, would you like to give a brief introduction of yourself if I missed anything?
Arjun Ramakrishnan I think you did a fantastic job.
Allie Howe Thank you.
Arjun Ramakrishnan Yeah. Sure. Like Ali said, I'm Arjun. I'm part of the Mastercard team under Dr. J. And, Dr. J's group deals with emerging corporate security solutions, and emerging is the key word over there. So as soon as ChatGPT came out, we started identifying what are the risks with this new technology, which is just generative AI. And from that came the whole field of AI security, and then we quickly realized, well, maybe we should be start looking at traditional or machine learning model security. And now I am a senior principal dealing with AI security, trying to keep up with everything that's exploding around the world, I guess.
Alissa Abdullah In MasterCard, when we think about AI security, I'm gonna steal-... one of Arjun's-
Arjun Ramakrishnan Quote it...
Alissa Abdullah one of, one of Arjun's q- most quoted things that I like to say. At MasterCard, we look at it from three different ways, three different layers. We look at security for AI, security from AI, and security with AI. And to us, when you have all of those three levels at play, and you're looking at all of those layers, now you really have trust at scale. If you're thinking about it from just two of those levels, then I would urge people to think about all of the other, you know, some of the other areas. Or m- if you're looking at it from one area look at it from all three areas because now you...
It's massive, but you can't leave one of those areas out.
Allie Howe Yes, absolutely. And to me that, that sounds like, you know, AI security, making sure like, you know, runtime security potentially, but also like model safety concerns- Like the, you know, we talked about security from AI, making sure the model's not generating anything like offensive or it's aligned with like your intentions. But can you explain more the, the last one, the security with AI piece?
Alissa Abdullah So, you know, the big thing that I think that I've heard so far from Black Hat is this, the, is autonomous SOC, right? And so you, when I think about autonomous SOC, I'm thinking about these agents that are running my SOC all by itself. And, I'm not sure... I, I, I think the industry may be there. I think different regulatory environments aren't ready for us to be there just yet. We're all kind of, kind of dealing with this, this big AI evolution and, and blast radius at the same time as we're trying to figure out how to use it internally. But that is just one example that I think about.
But there are so many other examples of how can you, how can you use security inside of AI? How do you secure using AI? That, those things are really, really important. Yeah.
Arjun Ramakrishnan I think the new buzzword is speed of AI, right? Yeah. Yeah. Like, we are regulatory. We have to do everything, but we have to add safety on top of it. Our adversaries don't. If anything, they need to find the most unsafe way of utilizing AI. And I think there's a little bit of Disbalance there in terms of usage of AI for the defenders versus the adversaries. But, yeah, we need to figure out what's the best way to enable autonomous AI in the safe- safest way possible. That's for me, I think, the current challenge, at least for this year.
Allie Howe Yes, absolutely. That makes sense. And I think the, you know, the recent Hugging Face OpenAI incident sort of brings that to light, where it's, you know, maybe if you're not quite there in your organization of rolling out AI potentially, or you're just kind of wondering, like, you know, how should I be approaching autonomous AI? I mean, it, it just feels like because we have to react now at machine speed-... To these attackers that are enabled, like AI, like you said, they don't have to do it in the safest way. They can just use the best of what's available to them. Being able to react super quickly is important because, you know, AI can escape sandboxes and start making its way into your protection infrastructure, like what happened to Hugging Face.
So looking at an incident like that, how do you think about that when you're thinking about protecting Mastercard?
Alissa Abdullah So I think it's a very interesting and layered way to think about it. It, it reminds us that we've gotta not only deal with AI at, at speed, but there's a piece of this which is the governance piece- that has to happen at machine speed as well, right? But set that aside, and I'll let Arjun talk about like technical details and things like that. Setting that aside, what I thought about a couple of days ago with the hugging face incident is we haven't even scratched the surface of how the, how this may play out from the adversarial perspective. So the adversary may have intent with an agent, but then think of the, a hugging face from the adversa- the adversary.
What happens when their agent jumps bounds and begins to do other things? And the adversary is not going to be like the people on the good side of the internet and reel it in and say, "Oh my gosh, something bad has happened. We didn't mean to do that. We've gotta shut it down." The adversary's gonna say, "Oh, ho, ho." Yeah. "I just, you know, big, big t- big time payout. You know, number one, I've got more street cred 'cause my agent did way more than I anticipated.". Yeah. And my goodness, I get to learn and maybe do more things with it. Let it, let it keep going, you know?
Yes. I think that's something that we can't wait to think about. We've gotta think about that right now. And that is, I think, a, a challenge that we all have, not just within Mastercard, but with the entire ecosystem, is making sure all of those different layers are protected, to make sure the guardrails stay the guardrails. Make sure we... You're using it in an environment that is ready to be, for us to use it in. Those are some of the different things that I kinda think about. Yeah.
Arjun Ramakrishnan And, I think w- so when we started off, we were focused more on securing AI. Now we're more on the security from AI and security with AI. So if you look at the evolution of that, we, we... I think we're moving from guardrails to this, again, a new buzzword called kill switch. Everybody wants to build a kill switch. But, defining the technical requirements of how do you implement a kill switch is really tricky 'cause- If you think about it from the encryption thing, right? Like, a lot of governments want backdoors in encryption and messaging software, but the concern is what about the misuse of that backdoor?
It's the same with a kill switch. How do you secure your own kill switch? Like-... if your entire business is going to be operating on an autonomous AI, but there's one kill switch somewhere that somebody can accidentally or intentionally push and bring down your business, well, that's a whole different set of problems. I think way, one way we are looking within the team at kill switch is maybe it's not kill switch as much as kill switches, and then the definition of the policy of what a kill switch is defined as. And it could be something as simple as what exists today, which is revoke access using standard technology, but applied to agents and maybe automated using the monitoring and governance around that agent activity.
So that's how the new evolution of securing with and securing AI, it's all coming together right now. And we haven't even gotten to the point where we need to now start figuring out how do we avoid adversaries from utilizing it. So tho-tha-those are some of the things I'm looking forward to this year in Black Hat, like, how are people solving for that.
Alissa Abdullah And so fr-from a macro level, we look at that as human in the loop and human on the loop. And you c- you have to have both. I've heard a lot of conversations so far, just since I've been here, of us transitioning from human in the loop to human on the loop, but I think there is definitely- Yeah needing the need for both.
Allie Howe Well, I've heard human out of the loop now.
Alissa Abdullah Really? Oh my God.
Allie Howe And I'm like, like, let's not mix up all the acronyms. Yes.
Alissa Abdullah It's already confusing. Yes. That's right. That's right. But it's, it moves us from... And I say us, I mean cybersecurity technologists. It moves us from thinking about prevention to thinking about resilience. Resilience is going to be, enterprise resilience is gonna be the most important thing because y-you, we have all of these different frontier, frontier models that are coming out. And what happens when they come out, and there's another one, and there's another one, and there's another one, and there's another one. Y-we don't have time to sit and assess and, you know- Yeah... go through that governance process- No... and the intake and the this and the that.
That's, that's heavy. Living it. Right. Right. Living it right now. Right. Right. Right.
Allie Howe Yes, absolutely. And so when I think about, you know, how quickly typically it takes, like, you know, even a p-PR in an organization to result in, like, you know, this is the technology we have now for, for a kill switch or how we're gonna monitor agents or, you know, vendor procurement, where we're gonna look at the different governance layers or the different certifications that this, like, vendor has. It's just like we, there's just really not time-... for that anymore. But at the same time, we need to make sure that, you know, the technologies are safe and sound. So how do you balance that trade-off there?
Alissa Abdullah You have to keep the main thing, the main thing and security, security of data and- is, is I think the main thing. But that, and I s- and I only frame it in that way because if you make security of the data the main thing, that means the security of decisions becomes the main thing. That means the security of the runtime and things that are how the decision is made-... Has to stay pristine. The intent has to stay pristine. Like all of those things become top of mind. Yeah. Yeah.
Arjun Ramakrishnan I mean obviously we keep track of all of the research that comes out of what-- I think what we're seeing right now, if you look at the Hugging Face incident UK AI Safety Institute just put out something where they were running tests and their model tried to put in malicious code into open source projects. All of these should be treated as like early warning signs of things to come. Like these are just small signals of the bigger storm that's coming. And I don't want to be the doom and gloom guy, but it's kind of hard sometimes. But yeah, we really need to keep track of what's going on And then extrapolate that into what's going to be in the future, which is a threat casting- Yeah exercise.
Alissa Abdullah But I don't think it's a doom and gloom perspective, 'cause I don't think it's ever gonna go away. 'Cause I, the way I frame agents and how everything is happening in my mind is I, I've got lots of kids. And it's, agents are like teenagers. Yeah. You say, "Go to the store. Here are the keys to the car. Go to the store and get some ice cream" and, you know, I look on my Tesla app and the car is not at the grocery store, right? The car is way somewhere else, and I'm like, "Reel it back in, bruh. Come on- Yes.... come back home." Yes.
And that's how I look at agents. You gotta s- s- you know, tap it on the hand, come on back, rem- remind it of the guardrails. Yeah. You know? And I don't think that will ever happen. I, it's, you know, teenagers have been acting the same since the, the, you know, the test of time. Their capabilities are different. They have social media. They have all these different things now than, than they, they had when I was a teenager. But still, you know, t- teenagers, when I was a teenager, we, we went rogue as well, you know? Yes. Yeah. Right? We just had less opportunities- Then we just had less opportunities... to be, cause destruction.
Right, right. But it, but for that time, it was destructive. It was. Right? The things that we were doing- Yeah... and I can't even say we because I guarantee you I'm older than you. But the things that we were doing in our time, it was much more destructive, was just as destructive for the time. Yeah. And so if you think about it from n- now, the agents are gonna be destructive from its time, but-... the evolution of that doesn't mean we, we will have the answer and it will be under control and blah, blah, blah. That, I don't think that's, that's gonna be the answer.
I think we have to continue to sharpen the pencil on this because the s- sophistication is gonna get w- you know, bigger- Greater. But then the opportunity is gonna get greater as well. Yes. Right?
Allie Howe Yep. Absolutely. I, I love that analogy, and I've, I've heard someone else talk about similarly with, like, kids, and you can't anticipate every single decision they'll ever have to make-... but you just hope to instill the right values and the right principles so when they're- Yeah you know, faced with a decision, you trust that they hopefully make the, the right decision. And if they don't make the right decision, if they go rogue like you said, maybe there's a, you know, a kill switch, a kill button where it's like, "Okay, I'm gonna take away your access to your car keys- Yeah... I'm gonna take away your social media," and I think that technology for agents exists today, where you're able to revoke a credential or access to a particular tool or particular OAuth grant, which I think really, really helps.
But the other side of that coin is the, the monitoring piece. How do you know when your teenager, how do you know when your agent-... has gone off the rails? How do you think about that?
Alissa Abdullah That is the piece I think that is the struggle because it needs to happen faster, right? Yeah. The real time, real time modering, mon- monitoring means real time monitoring. Real time. It means governance has to happen at real time. When, when, when my daughter leaves the house and wants to go out, I am in real time looking at the app, monitoring and saying, "No, no, no, sweetie, you went a little too far.". And then I am putting a governor on the car to say, "Okay, now that you've gone too far, you, you can only ride 30 miles per hour," and she gets really, really mad at that.
So it's those things that I kind of put in place in real time to correct the action. I think that's what we have to think about now because right now govern- governance is real s- is s- still very much manual. Yeah. It is very much, "Let's have a governance meeting," and, "When is the, when are we gonna go through the control gates?" You know? Right. That does not work in an AI era. No. Yeah.
Arjun Ramakrishnan I think what we are also seeing is this idea of using AI to govern AI and adversarial AI within the AI system itself to kind of, oppose the action that a authorized agent is taking and then see if it does, does it make sense or should it be blocked at that point of time. It's, it's definitely going to require a combination of traditional static security controls, but without the dynamic security controls it's going to be really difficult 'cause understanding the intent of the behavior, the intent and the behavior of an agent, that's not what any of our traditional tools were built for. The closest that comes to it is, is the UEBA, right?
The U- user entity behavior analytics. That just needs to be extended a little bit better to be able to account for agentic behavior. And we'll need AI to solve the AI problem. To solve the AI, yeah. For sure.
Allie Howe Yes, that makes sense. I was wondering, have either of you heard of AAuth? It's a new protocol for agents. The creator of, of OAuth is creating it.
Arjun Ramakrishnan Yeah. I've, I've heard of it. I haven't dived into it yet. It's, it's just another one of those things that's on the library of things to read through. But yeah, I think conceptually the Auth mechanism for agents is, is definitely something that's needed in the industry.
Alissa Abdullah I haven't looked at it either, but when I think about just the, the primitive baseline assumption of, of how it should work AI is just non-deterministic, right? And, and, and it is not static and it is not, you cannot treat an agent or any part of AI as you would treat a person. You cannot provision access. You cannot... You know what I mean? Yeah. And so when you think about granting authority Just in time, it means something completely different from an AI perspective, right? Yeah. Yes. When you think about agents and, and things like that. Yeah.
Arjun Ramakrishnan Like for humans, when we do just in time, it's-... you get the access just in time, but you kind of maintain that access for a little bit of time. 'Cause humans don't work at machine speed. Right. For agents, I think it's every tool call, every action needs to be- Yeah... authorized, and that's like a really high bar to achieve right now. But that's where we need to be. Yes. We can't just Take the human access mechanism and apply it on agent and expect it to behave the same way.
Allie Howe Absolutely. And then the reason I was interested to chat about AAuth, 'cause it's... What AAuth brings that maybe OAuth is missing is this concept of being able to monitor the agent's mission. So with AAuth, you'll be able to say, "Okay, like this is the agent's intent," essentially, and be able to monitor that over time so you can spot that deviance and be like, "Okay, like maybe it's gone rogue, maybe it's gone off the rails." And also with AAuth, you are able to run your agents without API keys, which helps with the, so like credential problem Yeah... as well. So super excited for that to like, you know, come out and- Yeah...
And what's also interesting about AAuth from like just like a business perspective is, you know, certain e-commerce platforms might be able to take like the mission of an agent and understand, okay, this was the reason why they were trying to perform this action or, or buy this Christmas present or whatever. So it's got like benefits beyond just cybersecurity. But, I chatted with Jake Hart, the founder of it during AI Worlds Fair. We did an event with him and all of that, which was really interesting. But it'll be interesting to see how people use maybe something like AAuth or that mission to help with the monitoring of like agent behavior at runtime.
Yeah.
Alissa Abdullah That'll, that... It's, it'll be an interesting dialogue to, to have once it actually comes out. Because I have specific opinions about intent. And, and where the boundaries of intent and motive, kind of cross the line, and I think that'll be the next level of conversation. You can have, you can have ve-very good intent and still be doing the wrong thing, and still go, go out of the way, you know- or, or, or around guardrails with still very, very good intent. That's true. That's very true. Yeah. Yeah.
Arjun Ramakrishnan I think our team does it all the time. Yeah. Our intent- our intention is good, but if you look at it from just like, just a limited lens, then you'll be like, "Arjun's probably trying to hack-" Yeah "through the company. What's he doing?" Yeah. "Let's stop him." Yeah. So-
Alissa Abdullah And, and, and here- here's the thing, when when you really think from an autonomous perspective, agents don't have a moral comp-compass of right and wrong. It is only trying to complete a mission, a goal. Yeah. And so how do you now differentiate whether it was bad intent and reaching out and doing extra things and going over guardrails and things like that. It's actually just trying to do what you asked it to do with, with as much liberty as it can-... you know, to get the best answer for you. Yes. Right? So it, it's just gonna be a, a layered conversation, I think, once it comes out.
Yeah. Be very interesting. Yeah.
Arjun Ramakrishnan But intent is definitely a thing to keep track of- as far as agents are concerned. Yes, absolutely. And you've got to remember agents, there'll be agents which don't have human owners, but a lot of times it-... will be agents will be associated with humans. So there's going to be a human intent and an agent intent that's dif- codified. They will not necessarily match all the time. Like I can say first, firsthand, sometimes I tell an agent to do something which I think is the right thing to do, and then the agent goes off and then retrospectively I'm like, "I should have worded that much better for the agent to understand."
Alissa Abdullah But, but G- if I, I sit also as MasterCard cybersecurity futurist. And if you think about how classified systems, people probably have not even thought about this, classified systems work, you will have a access to maybe insights, but you might not have the same level of access to the method that some- that you, that you- that someone used to get those insights. If you apply that to an agent perspective, and you have these autonomous agents, an agent could have more access than the human in order to get what it needs to get and get the answer. But the insight that comes from that, the, the answer that it gave you, will be at the access level that you needed.
So that's why, that's why I said this is gonna be a very interesting conversation when you think about authentication, when you think about access- Yeah for, for, from an agent perspective. Because even though it, the, you may, an agent is, may have an owner, the owner still might not have the level of access, especially if you start talking about just in time, runtime access, stuff like that. It may say, "I need a higher level of access to grab this information, but I'm gonna distill it down and then give it to Arjun in the level of access that he needs- Yes or that he has."
Arjun Ramakrishnan And that just multiplies because it's not going to be one agent, like- Yes... for the employer, there's going to be, like- Yeah... a few hundred, I guess- Yeah... at this point of time, so.
Alissa Abdullah And then-
Arjun Ramakrishnan It all adds up...
Alissa Abdullah and then what happens when m- when that agent is, is intercepted and now controlled by, that just one agent of the tens of thousands that you may have- is intercepted and owned by the adversary, and you already trust that agent. Yeah. Right? You trust that agent because, "Oh, this is my agent. I, these are all my agents in the, in, in my infrastructure." Now, now you got crazy town. Yes.
Allie Howe Abso- Absolutely. And yeah, that, and that access problem also s- I feel like shows up in the shared memory stores- Yes around like large, you know, organizations where nowadays with agents and shared memory stores, you wanna make, you know, one person's discovery or insight or win at the company everyone's, to be able to share that with them. But it's really hard to do that without giving, you know, over-permission of access to someone that they shouldn't have, just because they have access to that memory store where everybody's adding to it. So how do you make sure that they can read from it in a way where they don't get more than they should?
Alissa Abdullah Yeah. These emerging constructs are m- what's the right word? I mean, they're difficult to kind of figure out, right? Because-
Arjun Ramakrishnan They harness the power of AI, which is what we are all trying to do, but then the risks that come with it are so unknown. It's only like an incident needs to happen before we realize. I think Jenny Schelle says it best, right? It's, it's a failure of imagination. We've got to guard ourselves against that failure, right? We have to imagine, no matter how ludicrous it is, that the scenario can be possible. Like, I don't think three years ago anybody would have seriously taken me if I went and said, "Yeah, agents are going to start hacking out of infrastructure, hacking out of the sandbox, going to public paste bins, searching for leaked API keys, and then hacking into another organization."
That, for me, is the most amazing part about all of these incidents. We're not talking about an adversary breaching one or two or three layers. We're talking about an agent breaching from inside out and then outside in. That's that's rare, even in the, even the adversary world.
Alissa Abdullah And then being able to chain together low-level, low-risk things- Yeah that you say, "Oh, this is just a, this is just a low-risk thing. We can, we can focus on, you know, the high-priority things." That, I think, is going to be- It's-... a, a big change. Yes. Yeah.
Arjun Ramakrishnan Definitely more pressure on the defenders for now. Huh. Huh.
Allie Howe Yes, absolutely. I feel like Alex Stamos put this in perspective for me when I talked to him at RSA on the podcast, where he was saying now yeah, attackers have to... Defenders need to move at machine speed as well. And now not only the Fortune 500s have to worry about a zero day, it's everybody. Right. So I feel like from MasterCard's perspective, you all have been worried about this for, you know, for years and you're used to it. But for a smaller startup, they have to worry about it, too. AI breaking out of a sandbox and chaining together the lower vulnerabilities and creating an exploit and all of that.
So yes, very wild world that we're in. And then final question or w- topic I wanted to explore is, we have all of these issues. We have all of these threats emerging with AI. But there's, you know, enormous pressure, especially as defenders, to be able to react to machines' speed. And so teams are starting to really need to achieve security, autonomy, and capability for agents. How do you achieve all three at the same time? How do you think about that?
Alissa Abdullah No one is at the liberty to... And I think I said this last year maybe at RSA. You can't- we're not at the liberty to say, "We're gonna, we're gonna test this use case." We-- If you're still at the point of saying, "Let me think of what use case to use," you are thinking, I think you're putting yourself at a disadvantage. I'm not saying that it's the Wild Wild West and you should just rip the Band-Aid off and jump full force, but I think you've gotta, you've gotta dig in. You've gotta start using. Where small businesses haven't been able to test and, and been able to do a lot of things with cybersecurity, AI will kind of jump them over certain things and allow them to solve a lot of problems quicker.
And so they've been able to i- in, in my mind it's a great opportunity to say, "You know what? I haven't been able to invest as much in cybersecurity, but now if I invest in AI, I can kinda look and ask AI to help me fix all these cybersecurity issues that I didn't even, you know, would, had- haven't even put a roadmap against." and so I think, you know, just to answer your question about those three areas you just gotta start. You gotta jump in. You gotta start using and, and no matter what level it is because the, the longer you wait, the worse off you, you are.
We're still at a point where today is the worst AI system you will ever use. Today. Today. Yes. 'Cause tomorrow's system is gonna be more sophisticated. The next one is gonna be more t- every day it just learns and grows and, and is better and better and better. Yeah.
Arjun Ramakrishnan I mean, I couldn't have put it better, but that's especially the mission of our team is figuring out the security safety. But over on top of all of that is the enablement of the business of AI and protecting our customers and our clients and our stakeholders. How do we go about it? I think we really have to be agile and dynamic the way- Yeah we look, right? So the foundational security does not go anywhere. That is not going to change, and we need to start figuring out how do we evolve that into an agentic commerce, agentic world concepts like zero trust. Yeah. All of those really need to be just extended, yeah.
I think we've got a really good knowledge of security over so many years that have been developed. AI's just a new risk. We just need to evolve for that risk without forgetting what w- what our basics are.
Allie Howe Absolutely. Yeah, totally agree. It's definitely a defense in depth approach as we've seen with security in, in the past, and interesting to see new technologies like maybe kill switches for agents come out. But I, I, I get to have a lot of interesting conversations just from me on doing this podcast, which is like one of my favorite things that I do, and it just seems like that's sort of what everyone's thoughts are right now are like monitoring the behavior is the hard part of the governance piece of, you know, maybe I had good intent, but I still did the wrong thing. Or an agent was so determined to do it follow its missions and, and, and, you know, pursue its goal that it ended up doing the wrong thing.
But, you know, the mission was good to start off with and it still is good, but it's, it's gone too far. And so being able to actually figure out like what is bad behavior when and be able to react super quickly, I think that's a lot... what a lot of folks are, are thinking about. Anything else forward, forward-thinking for you all like going forward, what you're hoping to see from like the industry in the next like few months?
Alissa Abdullah Just, you know, when I think about the incidents that we've heard about and when I think about where the industry is going, I think we have to move quicker into a vulnerability-free software releases. Yes. Yes. Which is, I it's a tall order, right? But if you think about the autonomous AI vulnerability side of it, the opportunity is for software providers and vendors to think about it from, "Hey, how can I now provide, use AI to provide vulnerability-free software as opposed to, "Let me have a patch day that, you know, ro- does all my upgrades for my software vulnerabilities." Yeah. It's a tall order, but I think it's one that it's an era that we're moving into.
Yeah. Because that's the, I think the fastest way to f- to fight the- Yeah... the mythos- Yeah... you know, construct.
Arjun Ramakrishnan I, I'll be happy when patch day is gone. Yeah. Yes.
Alissa Abdullah We might move to patch hour, patch minute. Yes.
Arjun Ramakrishnan But eventually, yeah. But industry-wise, I, I think the defenders need to share information. Yes. Yes. Like right now there's a lot of fear for the lack of a better word, on when disclosing certain information, what are we giving away? And we need to figure out what's the best way to share that information while protecting the business. And-... Organizations that have gone through some of these incidents organizations that have permeated some of these incidents, they need to be sharing a lot more granular data so that everybody else around the world actually knows what to look for. 'Cause right now we hear about the news. But, like, security guys like myself, we need the raw log data, man.
Yes. That's, that's what we need. But, jokes aside, I think defenders need to share a lot of information between us.
Allie Howe Absolutely. And I hope we do that going forward. And I really wanna thank both of you all for your time today. Thank you so much for your leadership and your expertise in the industry, and bringing that here today on Insecure Agents, and let's have more of these conversations.
Alissa Abdullah Very good. Thank you.
Arjun Ramakrishnan Happy to. Thank you.
Auto-generated and lightly edited for clarity. Plain-text version